8.8 Million Danish Identity Records Copied via Legitimate Company Login
October 6, 2026 · Frisian News
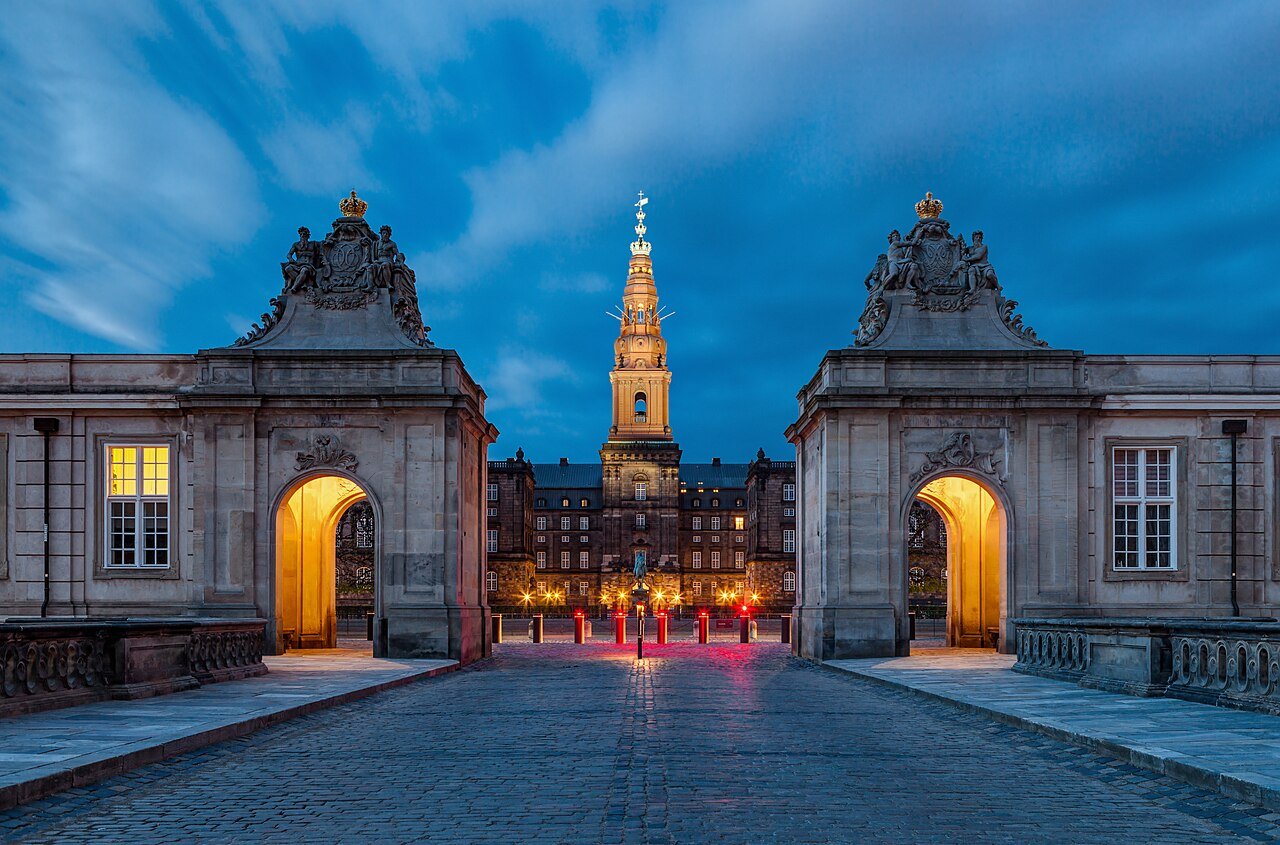
Photo: Wikimedia Commons
Unknown intruders copied names, addresses and CPR numbers for 8.8 million people from Denmark's central population register during September 2026, the government confirmed on October 5. The breach exploited a private company's lawful access to the system, not a technical vulnerability.
8.8 million records from Denmark's central population register were copied by unknown intruders during September, the Danish Ministry of Research, Education and Digitalisation confirmed on October 5. The country has about six million residents. The register holds 11 million entries in total, including the dead and those who have moved abroad, according to the ministry's statement as reported by brusselssignal.eu.
The three fields taken were names, addresses and CPR numbers, Denmark's permanent 10-digit personal identification numbers that run through every citizen's tax, health and banking records for life. The ministry told brusselssignal.eu that those fields had been copied, not merely viewed. Because the number is permanent, the exposure does not expire when the news cycle ends.
No technical exploit opened the system. Intruders used the lawful search access belonging to one unnamed Danish private company, according to the ministry's statement as reported by cybernews.com. Under Section 38 of Denmark's Civil Registration Act, reported by cybersecuritynews.com, private companies with a legitimate interest may query the register for a defined group of people identified in advance. That verification channel, built for routine business use, became the attack path.
Datatisynet, Denmark's data protection authority, said a very large number of automated lookups hit the system, according to unboxfuture.com, pointing to scripted harvesting rather than manual browsing. TV 2, cited by unboxfuture.com, reported the access ran for 10 days in September. Analyst Nathan Davies-Webb of Acumen Cyber, quoted by unboxfuture.com, calculated that the breach reached roughly 80 percent of everyone ever registered in the system. One company's credentials, in 10 days, exposed most of a national archive.
The CPR administration detected irregular behaviour on the evening of October 2, according to cybernews.com. The access had already run during September. Authentication was present throughout. The access itself was lawful on its face. The perimeter held while the front door was used exactly as designed.
Minister Christina Egelund called it "a deeply serious incident" and briefed parliament's Business and Digitalisation Committee, according to brusselssignal.eu. She ordered a full security review of the register. The company's access has since been blocked and the arrangement ended. The case was reported to Datatilsynet on October 4 and passed to the police. No suspect has been named and no motive given.
This is not an isolated pattern in Europe. Between May and August this year, a hacker calling himself ZeroBytes took tax files from France's public-finances directorate using stolen passwords and a compromised surveyor's login, exposing data on about 353,000 individuals and 252,000 firms, brusselssignal.eu reported. France's national cyber security agency ANSSI, in a September report cited by brusselssignal.eu, attributed the entry to absent multi-factor authentication, below-standard passwords and work accounts used from personal devices. The European Union's NIS2 directive, which member states were due to write into national law by October 2024, extends security duties to public administration. The rules have not closed the gap between the volume of data now held centrally and the access controls governments actually apply.
When one company's login can empty most of a nation's identity archive in 10 days, the question is not whether the perimeter held but whether it was ever drawn in the right place.
Published October 6, 2026 · Frisian News